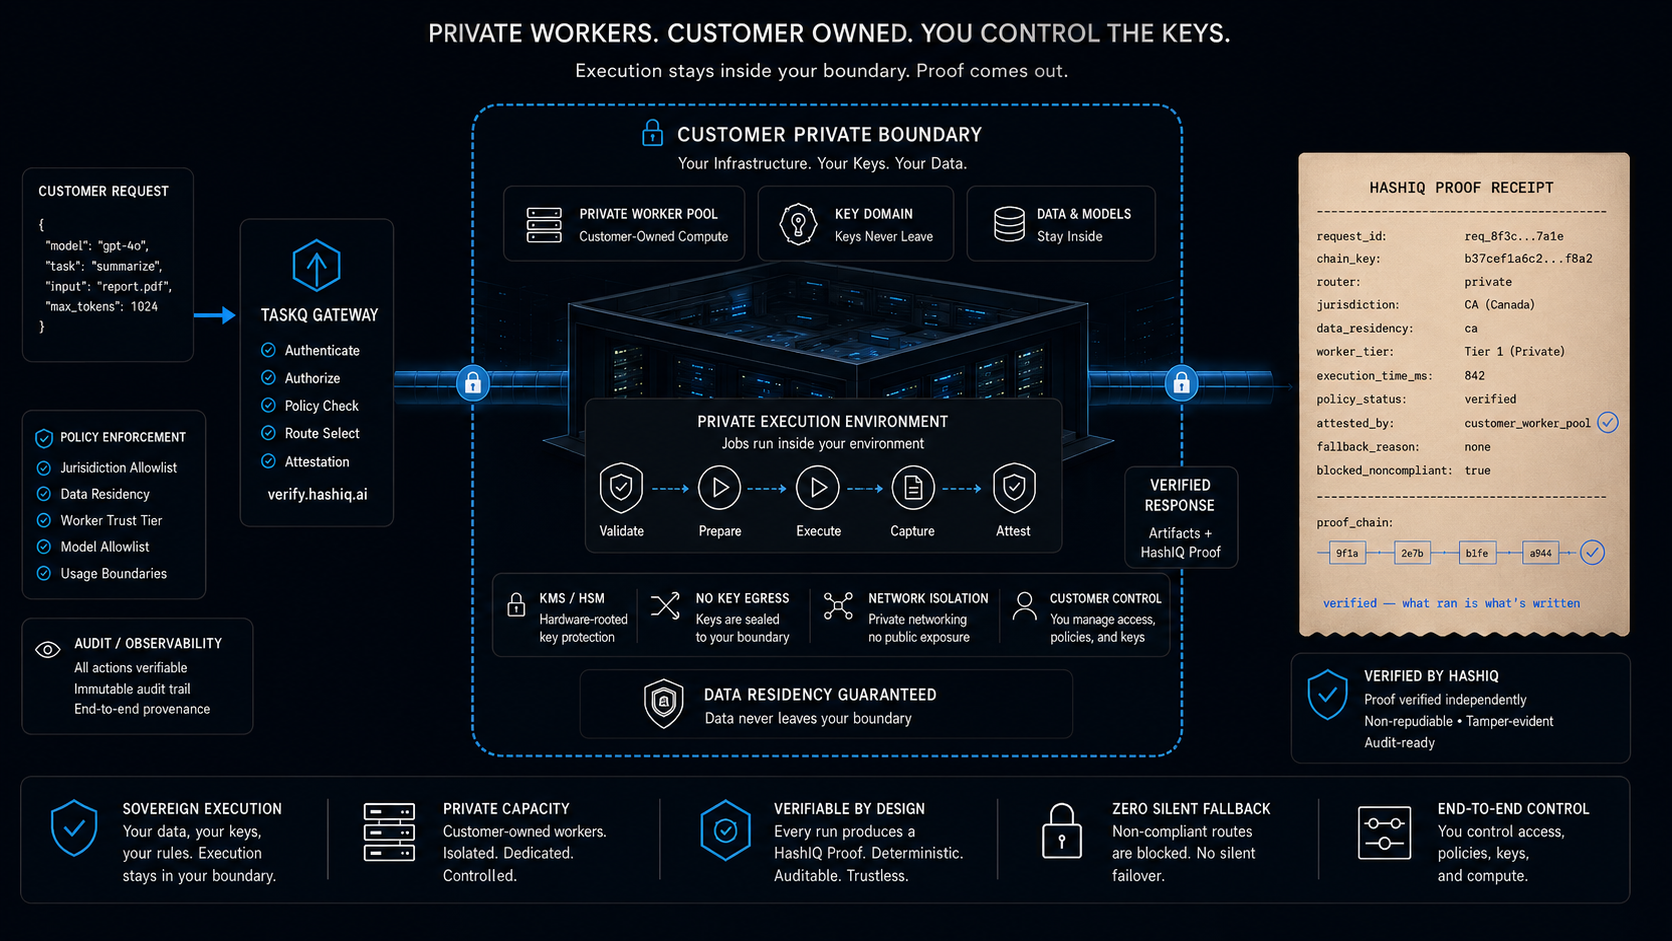
Private Workers let a customer run AI jobs on owned or dedicated capacity while TaskQ handles authentication, policy placement, BYOK custody, HashIQ proof, reporting, and settlement.
The customer can own the worker pool, key domain, network boundary, and artifact storage. TaskQ provides the control plane that decides what may run, where it runs, which credential handle is used, and what evidence is written.
GPU nodes, CPU workers, private inference, secure enclaves, colo racks, or internal execution pools.
Gateway, policy, placement, leases, proof entries, audit reports, and verifier surfaces.
Every accepted, blocked, completed, failed, and exported job can map back to signed proof.

Private workers are for high-control execution where jurisdiction, custody, artifact retention, network path, or internal policy matters more than lowest available price.
Privileged analysis, document jobs, evidence summaries, and chain references tied to matter-safe identifiers.
Policy-bound jobs where residency, access logging, retention, and exportable proof matter.
Code, reports, logs, tickets, and artifacts that should execute inside a controlled environment.
The control-plane lifecycle stays the same. The difference is the worker pool and key domain belong to the customer or are dedicated to them.
Worker keys, capabilities, jurisdictions, artifact policy, health checks, and trust claims are registered.
Customer defaults force requests into the private worker pool when the workload requires it.
TaskQ acquires a private slot and opens a HashIQ entry before dispatch.
The completed job returns artifacts and a verifier-ready chain segment.
The objection is not always model quality. Often it is custody, routing, sensitive data, worker trust, and whether evidence survives procurement, security review, and audit.
Force sensitive jobs onto private capacity and record why the route was selected.
TaskQ becomes the control/proof layer instead of the system holding every sensitive artifact.
Bring internal GPUs, colo nodes, sovereign clusters, or dedicated workers into the same policy plane.
Bring your own worker pool, key domain, artifact store, and jurisdiction requirements. TaskQ provides the control loop and proof layer.